
Every secure connection depends on more than an encryption algorithm. The systems on each side must agree on how to identify one another, negotiate protection, exchange data, reject tampering, and handle failure. A security protocol turns those requirements into an interoperable sequence of messages and checks.
That sequence matters to network teams, identity architects, application owners, and fraud teams for different reasons. It protects the channel and establishes technical trust, but it does not automatically determine whether an authenticated request is safe for the business. Understanding both the protection and its boundary is the practical starting point.
Quick Answer: What Is a Security Protocol?
A security protocol is a standardized set of rules that systems use to authenticate participants, protect data confidentiality and integrity, establish keys or sessions, and verify that messages have not been altered or replayed. Examples include TLS, IPsec, SSH, OAuth 2.0, OpenID Connect, SAML, DNSSEC, and WPA3.
A protocol is not the same thing as the component that implements it:
- A cryptographic algorithm performs a mathematical operation, such as encryption, hashing, or signing.
- A security protocol defines when and how those operations and messages are used between parties.
- A security product implements one or more protocols and adds policy, deployment, monitoring, or response features.
- A security procedure tells people or teams what to do. The phrase “security protocol” is sometimes used this way in physical or organizational security, but the technical meaning is the focus here.
What Problems Do Security Protocols Solve?
Security protocols create predictable trust between systems that do not begin with an inherently trusted relationship. Individual protocols solve different parts of that problem, so a complete architecture normally uses several together.
- Authentication: Is the server, user, service, or device the party it claims to be?
- Confidentiality: Can an observer read the information exchanged?
- Integrity: Can a recipient detect whether a message changed in transit?
- Authorization and delegation: What may an authenticated party do, and can it act on someone else’s behalf?
- Freshness and replay resistance: Can an attacker reuse a previously valid message or token?
- Interoperability: Can independently built systems apply the same security rules and failure behavior?
The last point is easy to overlook. Security is not useful at scale if every integration invents its own handshake, certificate format, token flow, or error handling. Standard protocols allow teams to use common libraries, test known behavior, and replace components without redesigning every connection.
How Does a Security Protocol Work?
Exact exchanges differ, but many protocols follow a recognizable sequence:
- Negotiate capabilities. The parties identify supported versions, algorithms, or methods. Secure negotiation must prevent a downgrade to an obsolete choice.
- Establish identity or trust. A certificate, credential, ticket, assertion, key, or trusted authority helps a party verify who is involved.
- Create a session or exchange keys. The parties derive or obtain parameters that protect later messages.
- Exchange protected data. Encryption can provide confidentiality, while message authentication or digital signatures protect integrity and authenticity.
- Validate state and freshness. Sequence numbers, nonces, expiration times, token state, and replay checks help reject duplicated or out-of-context messages.
For example, TLS 1.3 defines a modern transport handshake and record protocol. Its security depends on the protocol design, the cryptographic primitives selected, certificate validation, implementation quality, configuration, and key management. A correct standard cannot compensate for an expired certificate, a leaked private key, or an application that mishandles the authenticated session.
Which Types of Security Protocols Matter Most?
The most useful way to compare protocol families is by the trust job they perform—not by treating them as interchangeable items in one long list.
| Trust job | Common protocols | What they protect | Important boundary |
|---|---|---|---|
| Web and transport security | TLS 1.3, HTTPS, DTLS | Data moving between endpoints | Does not judge whether the request is legitimate business activity |
| Network-layer protection | IPsec | IP packets and VPN connections | Deployment, routing and key policy still matter |
| Administrative access | SSH | Remote login, commands and tunnels | Stolen credentials or poorly managed keys remain dangerous |
| Delegated authorization | OAuth 2.0 | Access granted to clients without sharing a user password | Secure deployment still requires correct redirect, token and scope handling |
| Federated identity | OpenID Connect, SAML, Kerberos | Authentication and identity assertions | Trust configuration and session handling can fail outside the protocol exchange |
| Naming and email authenticity | DNSSEC, SPF, DKIM, DMARC | DNS integrity and parts of email authentication | None of them alone makes all content or senders safe |
| Wireless access | WPA3 | Wi-Fi authentication and link protection | Endpoint security and network segmentation remain separate concerns |
1. Transport and network protocols
TLS is the current foundation for HTTPS and many API connections. “SSL” still appears in product names and search behavior, but obsolete SSL protocol versions should not be treated as modern alternatives to TLS. IPsec protects traffic at the IP layer and is widely associated with VPN deployments. SSH protects remote administration and tunneling, replacing cleartext tools such as Telnet.
Teams comparing network layers can also review these types of network security and the separate choices involved in wireless network security.
2. Identity and authorization protocols
OAuth 2.0 is commonly misunderstood as an authentication protocol. The OAuth 2.0 authorization framework enables a client to obtain limited access to a protected resource, usually through access tokens. OpenID Connect adds an identity layer for authentication. SAML exchanges assertions for federated identity, while Kerberos uses tickets in trusted network environments.
Choosing among them requires more than matching acronyms. The application model, client type, token audience, session lifetime, revocation needs, trust boundaries, and implementation libraries all affect the decision.
3. Name, email and wireless protection
DNSSEC helps a resolver validate DNS data, but it does not encrypt every DNS query or certify that a destination is benevolent. SPF, DKIM, and DMARC address different parts of email sender authorization and message authenticity. WPA3 strengthens wireless access compared with older generations, but migrating a mixed device fleet may preserve legacy fallback risks.
These examples show why “use a secure protocol” is not a complete requirement. A team must specify the asset, attacker, trust boundary, supported versions, and acceptable failure behavior.
Where Secure Protocols Still Leave Risk Gaps
A protocol can work exactly as designed while the larger transaction is still harmful. Encrypted traffic can carry credential-stuffing attempts. A valid OAuth token can be used by a compromised client. An authenticated session can submit automated registrations, scrape inventory, or abuse a promotion. The protocol confirms technical properties; it does not infer business intent.
Common residual risks include:
- Legacy fallback and downgrade paths: Compatibility settings can reopen weaker choices.
- Configuration and lifecycle failures: Certificates, secrets, signing keys, scopes, and trusted issuers require rotation and ownership.
- Endpoint or session compromise: Secure transport cannot repair malware, stolen tokens, or unsafe session logic.
- Limited context: A valid identity or connection says little about device history, interaction behavior, velocity, or coordinated abuse.
- Blind allow/block decisions: A technically valid request may deserve a challenge, rate limit, review, or narrower permission rather than unconditional access.
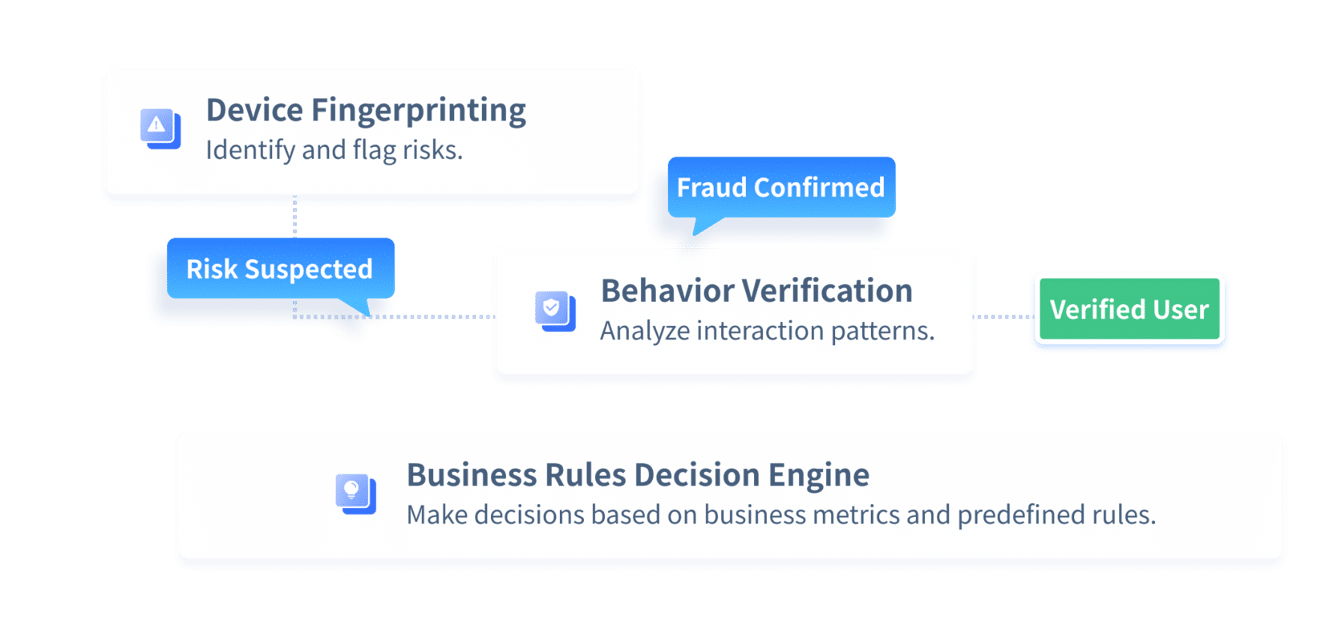
This is where application-layer risk controls complement protocols. GeeTest can combine device fingerprinting, behavior verification, and business rules to evaluate context after the connection is encrypted and an identity flow has completed. The goal is not to replace TLS, OAuth, or identity infrastructure. It is to decide whether a protocol-valid interaction should be allowed, stepped up, limited, reviewed, or blocked.
For a deeper look at the device signal layer, see how device fingerprinting enhances security.
How to Evaluate a Protocol Stack in Practice
1. Match each protocol to a trust job
Start with data flows rather than product names. Identify the parties, assets, network path, identity source, expected actions, and attacker capabilities. For each flow, document which control provides confidentiality, integrity, authentication, authorization, replay resistance, and audit evidence. A blank cell is more useful than a vague claim that the stack is “secure.”
2. Check lifecycle, interoperability and observability
Ask how the organization will operate the protocol after deployment:
- Which versions and algorithms are allowed, deprecated, or blocked?
- Who owns certificates, secrets, signing keys, metadata and trust anchors?
- How are rotation, revocation and emergency rollover tested?
- What happens when negotiation, validation or an identity provider fails?
- Can logs distinguish a handshake failure, policy denial, expired token, replay attempt, and application rejection?
- Are mobile, browser, API, partner, legacy and machine-to-machine clients tested separately?
The most expensive weaknesses often appear in these boundaries. A protocol choice may be sound while certificate renewal fails, a partner cannot rotate metadata, or monitoring collapses several unrelated errors into one alert.
3. Add controls for intent and business risk
After the protocol inventory, map the decisions it cannot make. Registration, login, account recovery, checkout, inventory access, API consumption, and content collection each have different abuse economics. The response should match the consequence: allow low-risk traffic, gather more evidence, trigger adaptive verification, reduce privileges, rate-limit, queue for review, or block.
| Review question | Good evidence | Warning sign |
|---|---|---|
| Does every protocol have a named trust job? | Data-flow and control map | A long protocol list with no threat model |
| Are versions and keys governed? | Owners, rotation tests, deprecation dates | “Automatic” renewal with no failure drill |
| Are failures observable? | Structured logs and distinct error states | One generic authentication error |
| Can policy use context? | Device, behavior, velocity and business rules | Every valid session receives the same trust |
| Is response proportional? | Allow, step-up, limit, review and block paths | One global allow/block threshold |
Final Takeaway: Protocols Are a Baseline, Not the Whole Defense
Security protocols make interoperable digital trust possible. The right stack protects connections, identities, names, messages, and delegated access, but it remains effective only when versions, keys, sessions, logs, and fallback paths are actively managed. For high-abuse workflows, add context and policy controls that can judge intent after protocol checks succeed. If your team is seeing protocol-valid automation or account abuse, GeeTest can help map device, behavior, verification, and business-rule controls to the affected transaction paths.
Frequently Asked Questions
1. Is SSL and TLS a protocol?
Yes. SSL and TLS are cryptographic communication protocols, but modern deployments should use supported TLS versions rather than obsolete SSL. “SSL certificate” remains common shorthand even when the actual connection uses TLS.
2. What is the difference between WPA, WPA2 and WPA3?
They are generations of Wi-Fi security standards. WPA3 improves protections over WPA2, while WPA was an earlier replacement for WEP. Real migration decisions must also account for client compatibility, configuration, fallback behavior and endpoint security.
3. Can security protocols stop bots and account abuse?
Not by themselves. Protocols can protect the connection and verify technical credentials, but automated traffic can still follow the protocol correctly. Device intelligence, behavior analysis, rate controls, adaptive verification and business rules help evaluate intent and risk.
4. How often should an organization review its protocol stack?
Review it continuously through vulnerability, certificate and configuration monitoring, with a formal review at least when standards change, dependencies reach end of support, a trust relationship changes, or an incident exposes a control gap. The appropriate cadence depends on system criticality and change rate.